Your brand and customers
are being targeted right now.
Search by enterprise name or domain (e.g. abc.bank) to expose active phishing gateways, counterfeit Meta sponsored ads, and Roman-Urdu scam campaigns before your customers lose money.
Designed for CISO Command Centers & Autonomous Brand Defense
Inspect the exact live deployment safeguarding Tier-1 enterprises: from the 0–100 Zero-Day Scoring Matrix and 1-Click Forensic Evidence Packs to Multi-Tenant SOC Governance.
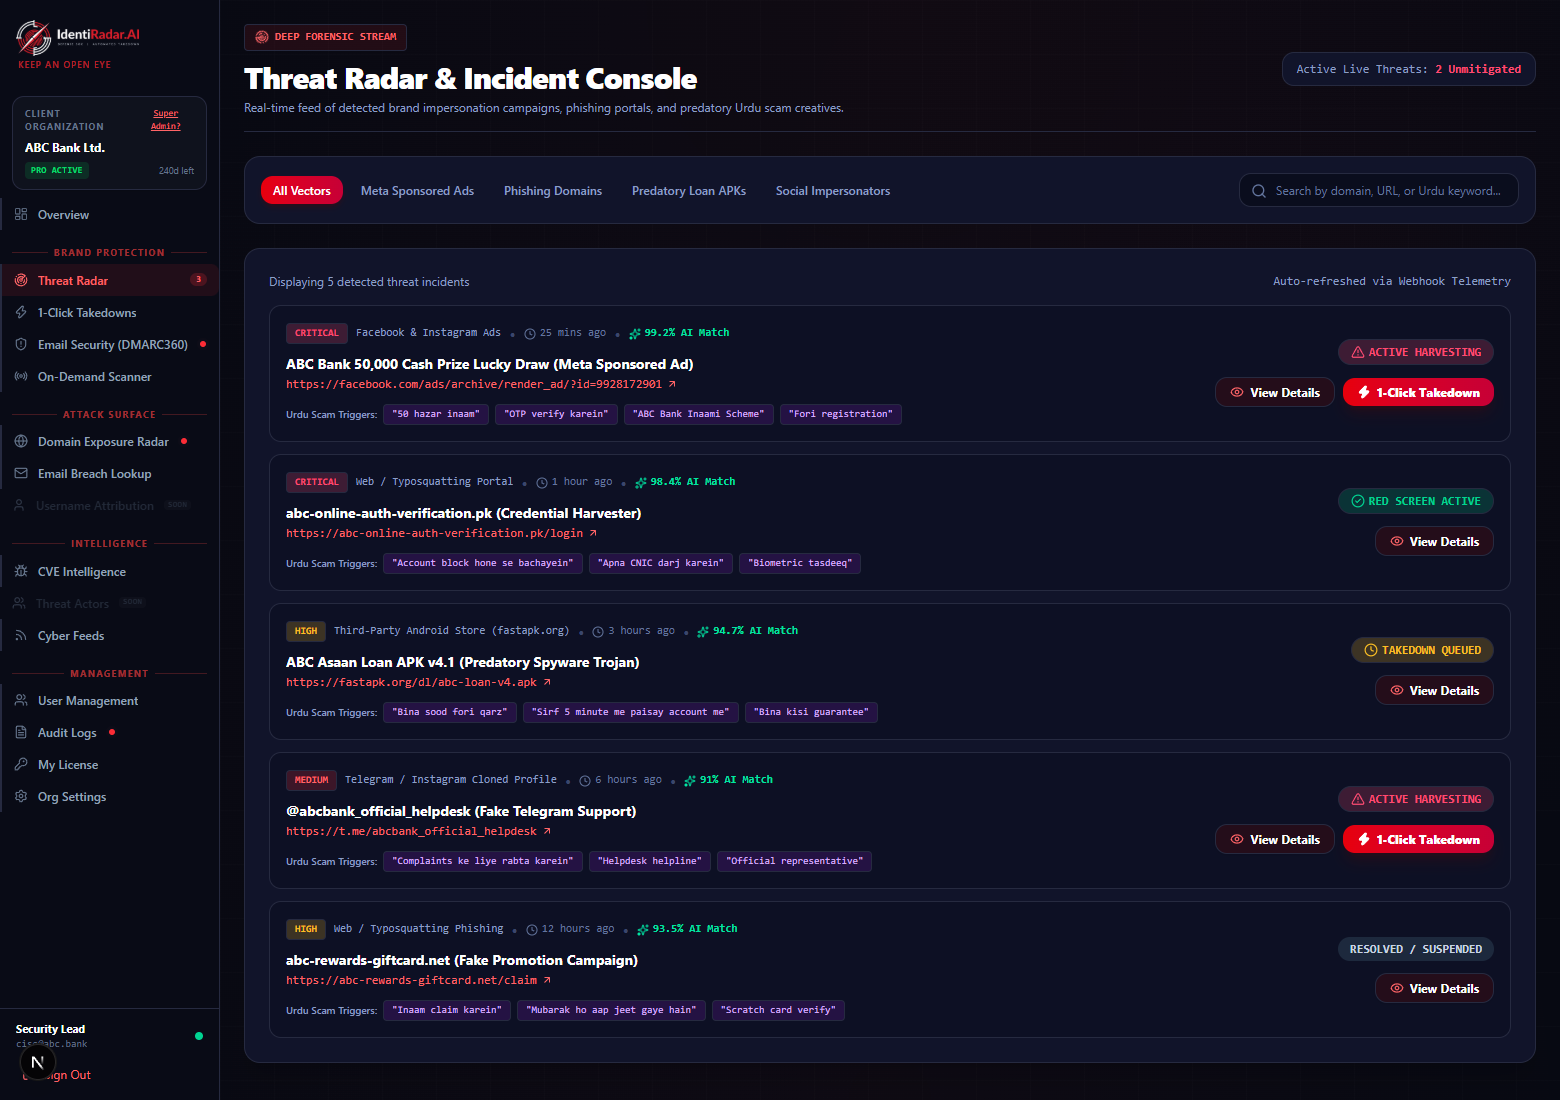
Surveillance across Social Ads (Meta, TikTok), lookalike domains, rogue APKs, and Dark Web chat channels.
Algorithmic threat rating combining pHash visual similarity, domain registration age, and phishing triggers.
UTC-hashed screenshots, HTTP HAR redirect tree, WHOIS/ASN logs, and trademark proof ready for legal action.
Tracks live mitigation state: Blacklisted in <15m → Ad Pulled → Host Suspended → Domain Seized.
Watch the Scam Neutralized Before It Steals a Single Customer.
From rogue Meta ads and typosquatted domains to malicious APKs — see how IdentiRadar’s autonomous pipeline detects, uncloaks, and takes down brand threats in minutes, not weeks.
Multi-Vector Autonomous Surface Ingestion
Continuous surveillance across 5 adversarial surfaces: Meta/TikTok Ad Libraries, Lookalike DNS & CT Logs, Rogue APK Repos, Underground Telegram Forums, and Spoofed SERP results.
Takedown Resolution SLA Speed Matrix
Select an enforcement vector below to inspect automated response protocols and channel speed guarantees.
Instant Browser Shield
Immediate warning red screen on Chrome, Edge, and Safari via Google Safe Browsing and Microsoft SmartScreen APIs before the hosting provider even checks their inbox.
Social Media Fake Ads & Pages
Direct automated abuse submission to Meta Graph API, TikTok Safety Desk, and X Brand Trust teams with cryptographic ad spend identifiers for immediate campaign termination.
Phishing Hosting Removal
Machine-readable abuse reports dispatched to Cloudflare, AWS, DigitalOcean, and offshore hosting providers with signed HTTP HAR logs and phishing origin headers.
Lookalike Domain Suspension
Fast-track legal takedowns with Namecheap, GoDaddy, Porkbun, and ccTLD authorities utilizing automated UDRP trademark certificates and forensic evidence dossiers.
Rogue Mobile APKs Takedown
Package hash & certificate collision dispatches to Google Play Protect, Apple App Store, and third-party mirrors (APKPure, Aptoide) to permanently block rogue installs.
Everything hackers see before they launch an attack.
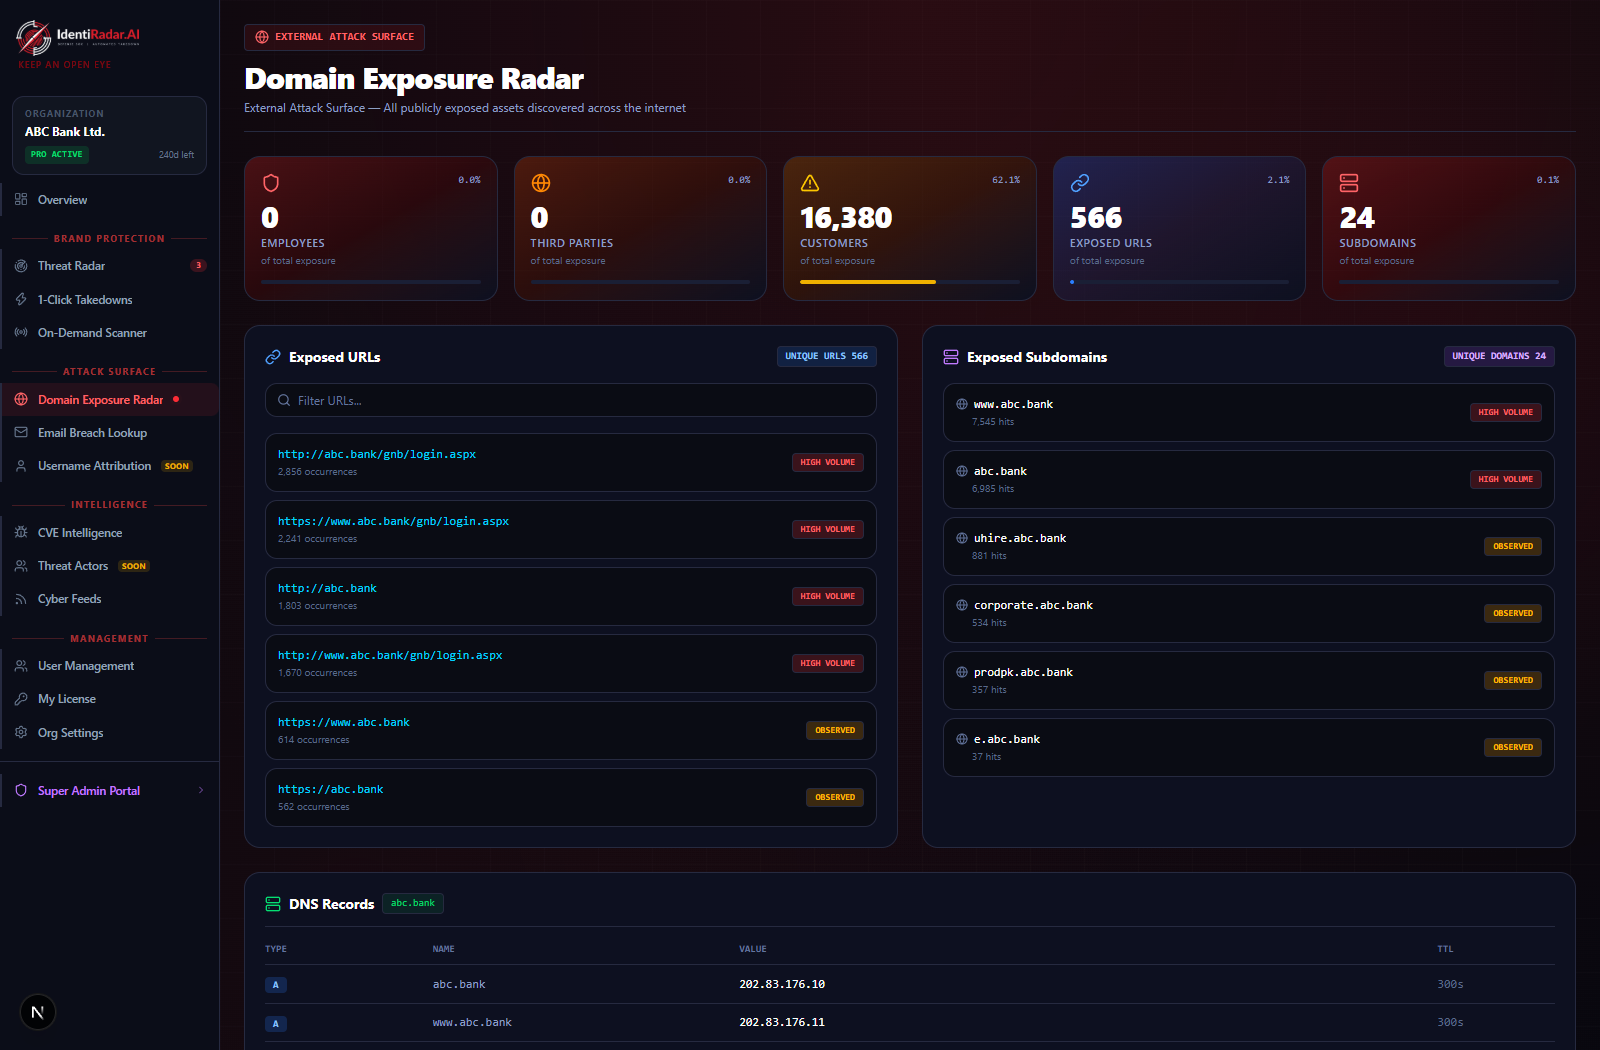
Most companies only monitor their primary website. Meanwhile, attackers exploit forgotten staging domains, unpatched subdomains, leaked executive emails, and rogue DNS records to breach the network.
DNS Dumpster & Certificate Transparency Enumeration
Passive scanning queries thousands of certificate logs without alerting the target.
Exposed URLs & Login Portals
Detects unauthenticated administrative endpoints and credential harvester mirrors.
Shadow IT & Orphan Cloud Hosts
Finds abandoned AWS S3 buckets, staging servers, and unmanaged partner portals.
Built to defeat the scams foreign tools can't even read.
Roman Urdu & Urdu Visual Scam Shield
Interprets localized Pakistani financial fraud phrases ("50 hazar cash inaam", "Account verify karein", "Bina sood fori qarz") through deep contextual NLP.
15-Minute Browser Red-Screen Poisoning
Direct integration with Google Safe Browsing and Microsoft SmartScreen triggers immediate bright red security warnings on Chrome, Firefox, and Edge browsers.
PECA 2016 Legal Evidence Packs
One-click cryptographically signed legal evidence dockets citing Pakistan Electronic Crimes Act Sections 13, 14, and 16, pre-formatted for PTA and FIA Cyber Crime Wing.
Predictable Security Investment. No $50,000 Surprise Bills.
Deploy comprehensive brand impersonation defense, 15-minute takedown SLAs, and full attack surface monitoring at a fraction of legacy vendor costs.
SME & Growing Brands
Essential brand protection for mid-sized commerce, fintech startups, and growing enterprises.
Financial Institutions & CISO SOC
High-velocity autonomous defense designed for commercial banks, digital wallets, and national retailers.
Critical Infrastructure & Telecom
Full-spectrum intelligence for telecom operators, government portals, and multi-brand conglomerates.
Need a Custom Plan or Tailored Regulatory Modules?
If your enterprise requires custom integrations (specialized core banking APIs, proprietary threat feeds, PTA/SBP regulatory compliance dockets, or on-premise proxy agents) that are not currently in our catalog, our engineering team will build and deploy custom modules within 10 working days at minimal cost.
From Rogue Ad Detection to 15-Minute Takedown
Visual breakdown of how IdentiRadar AI identifies, reverse-engineers, alerts, and terminates brand impersonation attacks autonomously.
Ingestion & Rogue Ad Crawling
High-velocity scrapers continuously query Meta Ad Library, newly registered homoglyph domains, rogue APK repositories, and Telegram scam channels.
AI Computer Vision & Roman Urdu OCR
GPT-4o Vision calculates brand logo visual similarity percentage, transcribes Roman Urdu fraud copy ("50 hazar inaam"), and flags OTP harvest fields.
WhatsApp & Multi-Channel Alert Relay
Within 12 seconds of confirmation, emergency alerts with evidence links and severity telemetry are dispatched to CISO WhatsApp, Slack, Teams, and SIEM webhooks.
15-Min Poisoning & PECA Takedown
Automated API pipeline injects Chrome/Safari red warning screens via Google Safe Browsing, drops Cloudflare DNS proxies, and dispatches signed PECA 2016 PTA dockets.
Upcoming Security Capabilities • Next Phase
Advancing from brand protection into autonomous adversarial simulation, cloud posture hardening, and threat intelligence orchestration.
Automated Asset Discovery
Continuous discovery, tracking, and topology mapping of domains, subdomains, IPs, SSL/TLS certificates, cloud storage buckets, and shadow IT assets across global networks.
AI-Powered Vulnerability Scanner
Contextual heuristic engine analyzing web applications, exposed service ports, and third-party dependencies to detect exploitable zero-day pathways before adversaries.
Autonomous Penetration Testing Agents
AI agents executing multi-step autonomous red-team simulations against public endpoints, evaluating API resilience, token replay attacks, and authentication barriers safely.
Malware & APK Behavioral Sandboxing
Dynamic detonation chamber inspecting suspicious Android APKs and droppers, analyzing permissions, C2 callbacks, SMS interception hooks, and fake bank overlays.
360° External Attack Surface Monitoring
Comprehensive perimeter monitoring correlating misconfigured DNS records, dangling CNAMEs, expired certificates, and open management interfaces across entire subsidiaries.
Multi-Cloud Posture & Pen-Testing
Automated security auditing and adversary simulation across AWS, Google Cloud, Oracle Cloud Infrastructure, and Microsoft Azure environments.
APT & Campaign Tracking
Actionable attribution intelligence tracking global advanced persistent threats (APTs), financial fraud cartels, and targeted adversary Tactics, Techniques, and Procedures (TTPs).
Instagram, TikTok & X.com Fraud Surveillance
Continuous AI vision & NLP surveillance across Instagram sponsored posts, TikTok viral scam reels, and X.com (Twitter) cloned corporate handles to intercept deceptive brand campaigns and counterfeit customer support dockets.
MITRE ATT&CK Mapping & Hardening
Direct correlation of identified brand threats to MITRE ATT&CK enterprise matrices with specific defensive "Kill Switch" directives and posture hardening blueprints.
Exportable STIX / TAXII Threat Feeds
Curated IoCs, IoAs, and IoWs exportable via STIX 2.1, JSON, YARA rules, and REST APIs for native SIEM/SOAR ingestion into Splunk, Microsoft Sentinel, and IBM QRadar.
IdentiRadar AI vs Foreign Enterprise Scanners
Foreign providers charge $50,000/yr yet remain completely blind to Pakistani and GCC scam vectors.
| Capability Matrix | IdentiRadar AI | ZeroFox / Group-IB / CTM360 |
|---|---|---|
| Roman Urdu & Urdu OCR Detection | 100% Native NLP (Regex + Vision) | 0% (Completely Blind) |
| 15-Min Browser Red-Screen Injection | Automated GSB / Web Risk API | 24 - 72 Hours Delay |
| Pakistan PECA 2016 PTA Evidence Pack | 1-Click Signed Docket | None (US/EU Templates Only) |
| External Attack Surface & DNSDumpster | Included in All Tiers | Separate $15,000 Add-on |
| Annual Enterprise Price | Local PKR / Transparent SaaS Tier | $40,000 - $80,000 / year |